Client-side compliance for payment service providers
Your merchants inherit your compliance posture and ask you about theirs. An organisation layer, per-team separation and unlimited domains make that a product rather than a support burden.
Start for free
Talk to an expert
TL;DR
Payment providers and the client-side requirements
THE OBLIGATION
PCI DSS 6.4.3 and 11.6.1 have been mandatory since 31 March 2025 for any page where a cardholder enters, reviews or confirms card data.
THE SPECIFIC DIFFICULTY HERE
Merchants ask how your hosted fields interact with scripts on their own pages, and the honest answer requires visibility you may not have.
WHAT THE TAG PRODUCES
A script inventory with justifications, a weekly header change record, runtime blocking, and an evidence pack for your assessor.
Short on time? Merchant domains are unlimited, so compliance you resell is not a per-domain bill.
See pricing
Does payment providers need PCI DSS script monitoring?
Yes, if you operate any page where a cardholder enters, reviews or confirms card data, which includes pages that embed a payment iframe. Your merchants inherit your compliance posture and ask you about theirs. An organisation layer, per-team separation and unlimited domains make that a product rather than a support burden. Requirements 6.4.3 and 11.6.1 apply to those pages regardless of platform, and have done since 31 March 2025.
Where the exposure is
Merchants ask how your hosted fields interact with scripts on their own pages, and the honest answer requires visibility you may not have
A skimmer on a merchant's parent page reflects on you even when your iframe behaved correctly
Supporting thousands of merchant domains under one compliance programme is an organisational problem before it is a technical one
Merchants at different SAQ levels need different evidence from the same platform
What the inventory shows you
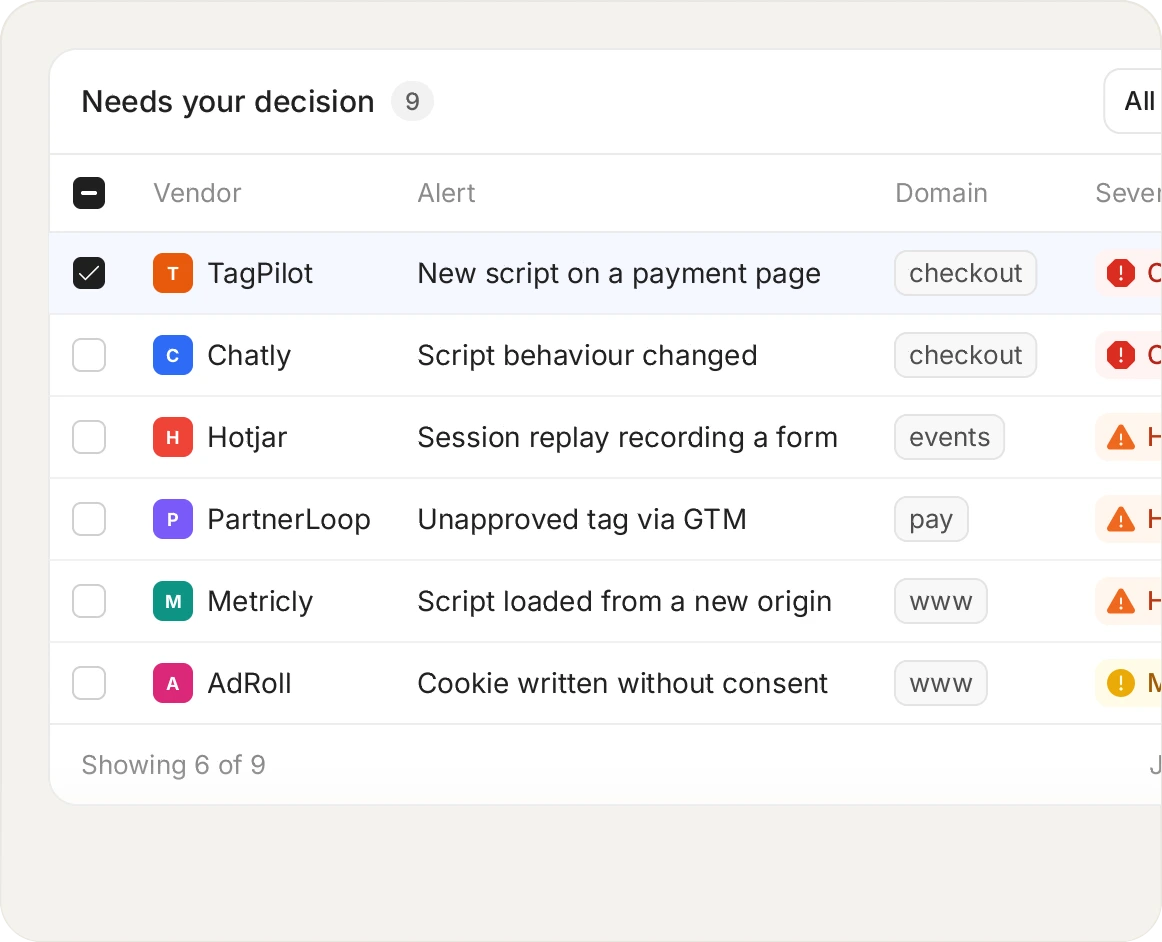
Every script on merchant payment pages, separated by team and organisation
Overlay and iframe-source tampering on the parent page around your hosted fields
Per-merchant evidence packs that a merchant can hand to their own assessor
Unlimited domains on every plan, because merchant count should not be a billing dimension
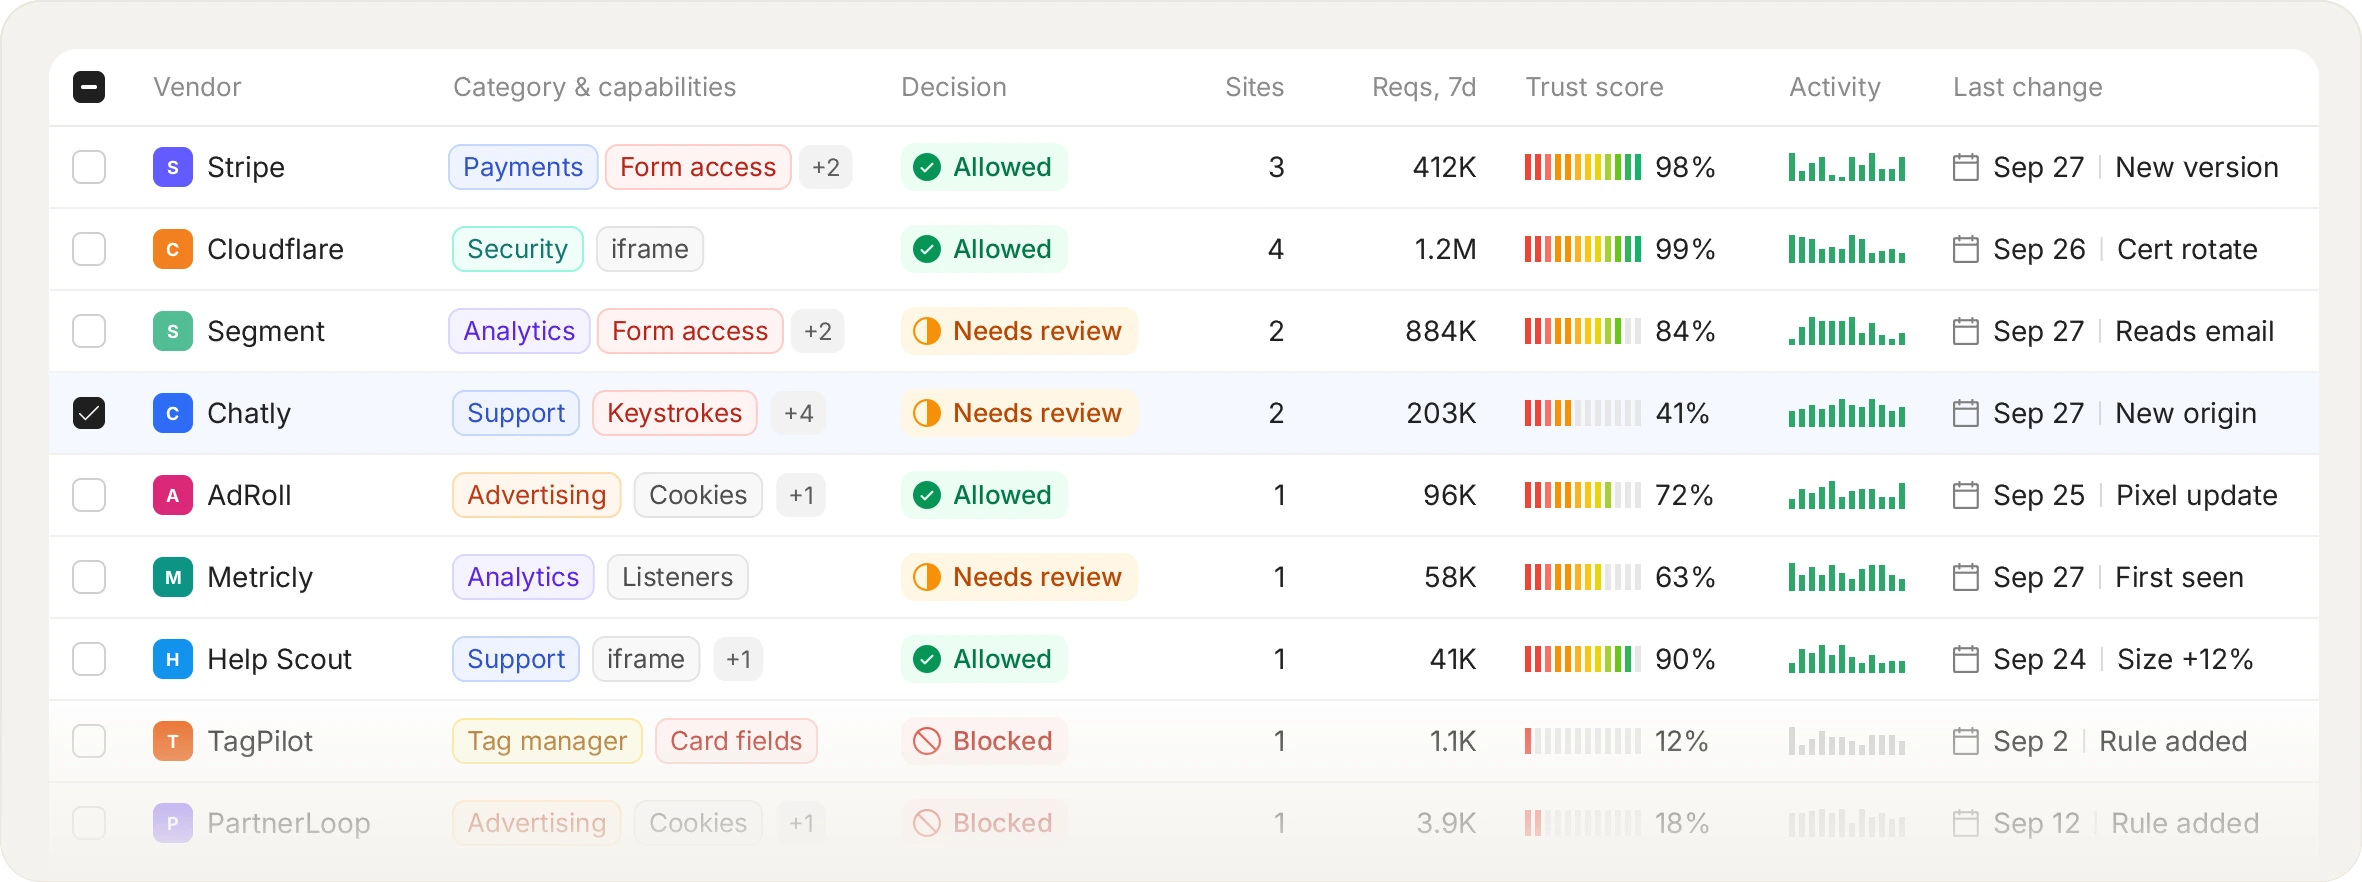
Requirement 6.4.3 is an authorisation record: every script on the payment page, where it came from, and why it is allowed to be there.
The two requirements, in this context
Frequently asked questions
Read the FAQ
Yes, and the organisation and team layer exists for exactly that. Each merchant can be a separate team with its own scope, evidence and alerting, under one organisation you administer.
No. Domains are unlimited on every plan. Page views are the only metered unit, so adding merchants costs what their traffic costs and nothing more.
Yes, and this is the case most worth covering. Your iframe protects the field itself. It does not protect the merchant's page around it, which is where an overlay or keystroke capture would sit, and which remains in the merchant's PCI scope.
Yes, per team, covering their own scope only. That is usually what their assessor asks for.
See the scripts on your own payment pages.
Free forever on 1,000 page views a month, no credit card. Unlimited domains on every plan.
Free forever plan. No credit card.